devtake.dev

#windows

RSS
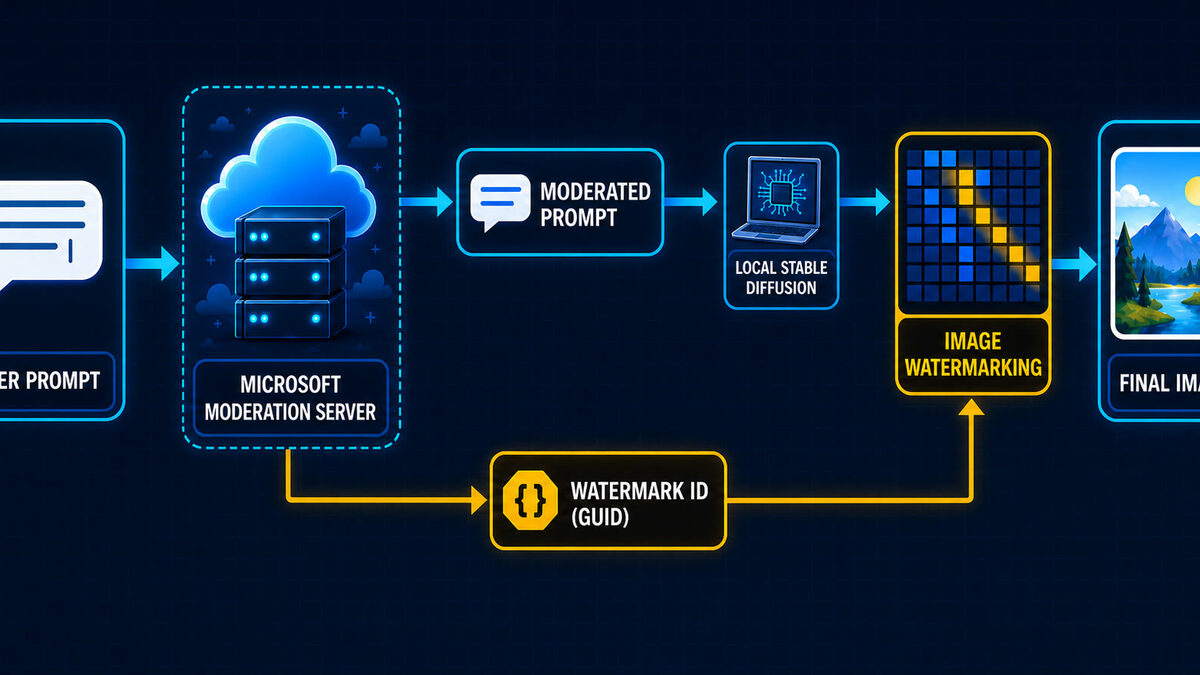
Data-flow diagram showing a user prompt going to a Microsoft moderation server, which returns a moderated prompt and a watermark ID GUID, with local Stable Diffusion generating the picture and an image-watermarking stage stamping the GUID into the final image
Security·

Server-issued GUID in the pixels: Paint's local AI generation still phones Microsoft first

Xusheng Li took apart Microsoft Paint's watermarking code and found the invisible mark is a per-request GUID issued by a Microsoft server before any pixels exist.
A physical computer keyboard photographed from above.
Security·

Microsoft fixed a record 570 flaws and still left a Windows zero-day unpatched

Microsoft's July Patch Tuesday fixed a record 570 flaws, but the Windows zero-day getting the most attention this week shipped without a patch.

Close-up of an AT motherboard showing the socketed BIOS chip and real-time clock, the low-level firmware where Secure Boot certificates live.
Security·

Secure Boot's 2011-era keys start expiring, cutting off boot updates on unpatched PCs

Microsoft's 2011 Secure Boot certificates started expiring in June 2026. Here's what breaks on Windows and Linux, and the one update that fixes it.

GitHub and Windows security composite with a warning overlay
Security·

GitHub banned the researcher dropping Windows zero-days. The code was already mirrored everywhere.

GitHub wiped Nightmare-Eclipse's account on May 23 after weeks of unpatched Windows exploits. The ban reopened the oldest fight in security: who decides what research gets hosted?

Windows logo composite with security-warning overlay
Security·

A USB stick now opens a BitLocker drive in 60 seconds. The researcher calls it a backdoor.

A pseudonymous researcher dropped two unpatched Windows zero-days on May 12. YellowKey bypasses BitLocker via WinRE; Microsoft has not acknowledged either bug.

Abstract Kaspersky illustration of a tampered software disk for the DAEMON Tools supply chain attack writeup
Security·

DAEMON Tools shipped a signed backdoor for almost a month. Kaspersky says one school in Russia got the second stage.

Kaspersky pinned a supply-chain attack on the DAEMON Tools installer dating to April 8. Thousands hit globally, dozens upgraded to a QUIC RAT implant via signed binaries.